Category: Network+ (N10-009)
The CompTIA Network+ (N10-009) certification establishes the essential baseline knowledge required to deploy and support enterprise-grade network environments. In modern IT ecosystems, engineers must seamlessly bridge physical infrastructure with software-defined networking, cloud interconnects, and zero-trust security postures.
This category provides clear, domain-aligned educational content and technical walkthroughs tailored to both aspiring network administrators and candidates preparing for the N10-009 examination. Explore step-by-step subnetting guides, protocol comparisons, routing and switching configurations, command-line troubleshooting workflows, and performance-based question (PBQ) review scenarios.
-
Tutorial: Cracking Legacy Hashes with GPU Clusters in 2026
Distributed Graphical Processing Unit (GPU) clusters execute parallelized offline brute-force and dictionary attacks to systematically reverse-engineer deprecated cryptographic digests, such as NTLM, MD5, and SHA-1. Security architects deploy these adversarial workflows during enterprise credential audits to quantify the exact computational fragility of legacy identity stores and validate the necessity of migrating to memory-hard key derivation…
-
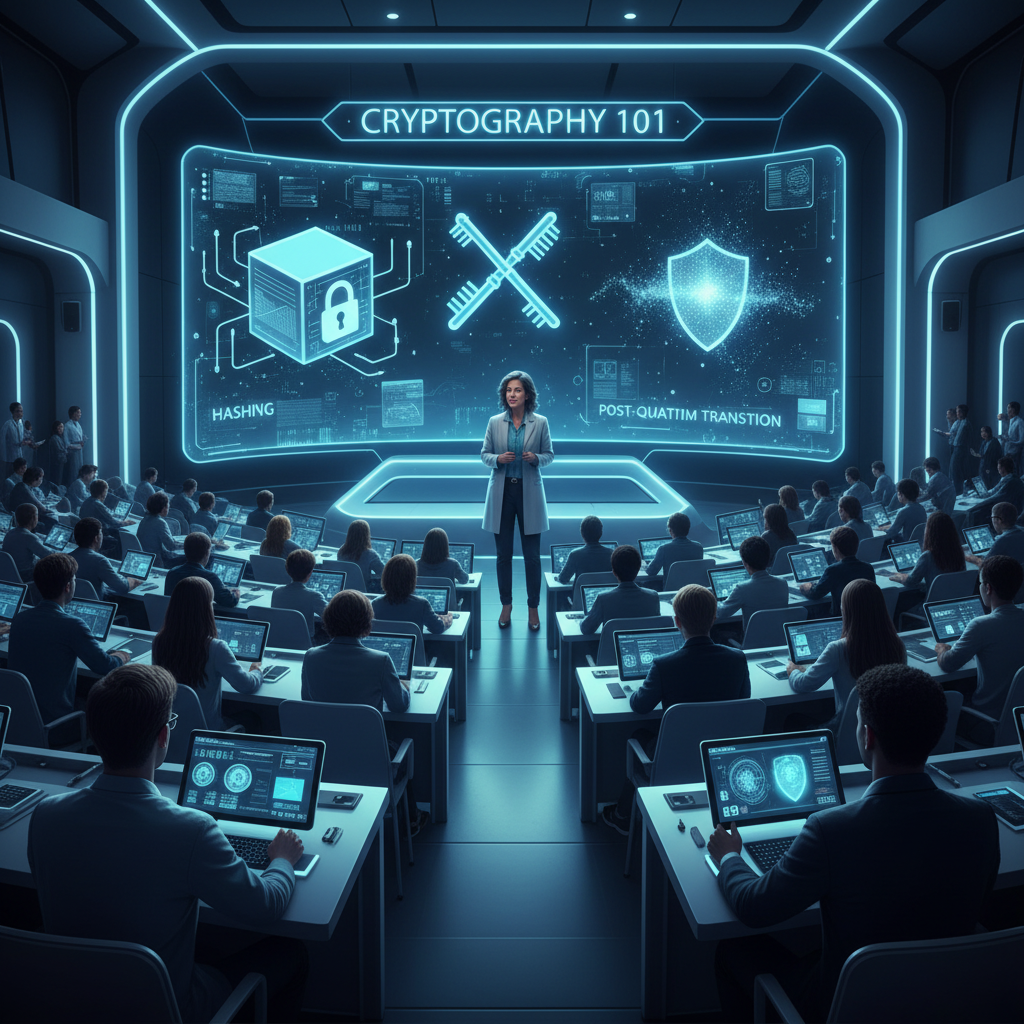
Cryptography 101: Hashing, Asymmetric, and the Post-Quantum Transition
Key Takeaway: Cryptographic primitives provide the mathematical foundation for enterprise data confidentiality, integrity, and non-repudiation. Security architects must implement robust hashing, deploy efficient asymmetric key exchanges, and proactively migrate to post-quantum cryptographic (PQC) algorithms to neutralize emerging quantum decryption threats. Hashing Mechanics and Integrity Verification Hashing algorithms execute one-way mathematical functions to map arbitrary input data…
-
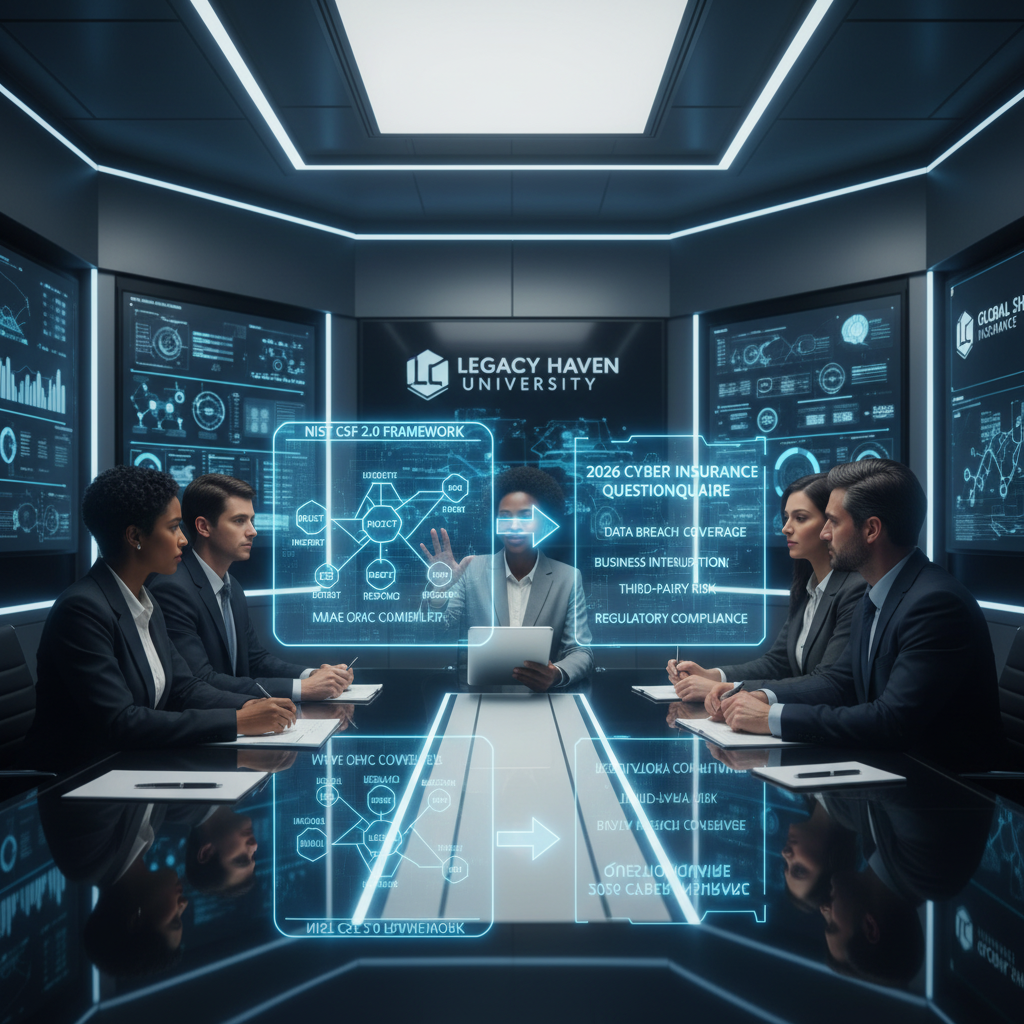
Mapping NIST CSF 2.0 to 2026 Insurance Questionnaires
Key Takeaway: Cybersecurity architectures leverage the NIST Cybersecurity Framework (CSF) 2.0 to provide cryptographic, real-time attestation to insurance underwriters. Static questionnaires have been deprecated; organizations must now deploy automated telemetry pipelines to map operational security controls directly to continuous liability risk models. The Govern Function as the Actuarial Integration Layer NIST CSF 2.0 introduces the “Govern”…
-
Cyber Insurance in 2026: Navigating AI Liability and Stricter Payout Clauses
Key Takeaway: Cyber insurance underwriters in 2026 require continuous, cryptographically verifiable proof of security controls. Organizations must perfectly align operational reality with policy attestation, as insurers will ruthlessly deny claims for basic security hygiene failures or poorly governed AI systems. Continuous Telemetry and Dynamic Underwriting Insurers have transitioned from static, annual risk assessments to dynamic, API-driven…
-
Lab: Analyzing AI-Obfuscated Malicious Payloads Safely
This laboratory guide explains how to build a secure, locked-down computer environment. Security agents use this safe zone to open, watch, and study dangerous computer viruses built by Artificial Intelligence (AI). We do this to figure out how the viruses work without putting our real computers in danger. ⚠️ DISCLAIMER: This laboratory guide is generated strictly for…
-
Next-Gen Malware Mechanics: Polymorphic AI-Driven Ransomware
Polymorphic AI-driven ransomware constantly alters its code to evade traditional security defenses while intelligently identifying and encrypting an organization’s most critical data. Infiltration and Code Mutation When this malware enters a system, it first evaluates its surroundings to ensure it is not operating within a security sandbox or an isolated analysis environment. Once it verifies…
-
Accelerating M&A Cyber Due Diligence with Agentic AI Scanning
During mergers and acquisitions (M&A), acquiring organizations must conduct rigorous cyber due diligence to uncover hidden vulnerabilities, shadow IT, and technical debt within a target company. Agentic AI scanners automate and scale this critical process, providing a comprehensive, dynamic assessment of the target’s attack surface prior to network integration. Unlike traditional, linear vulnerability scanners that…
-
M&A Cyber Due Diligence: Evaluating Target AI Supply Chains and Tech Debt
Mergers and acquisitions (M&A) fundamentally absorb the target organization’s hidden attack surfaces, requiring exhaustive cyber due diligence to quantify the risk vectors embedded within inherited artificial intelligence (AI) supply chains and compounding technical debt. Security architects executing the advanced threat modeling methodologies outlined in resources like the Ultimate Guide to CompTIA SecurityX must aggressively evaluate these systemic…
-
Social Engineering in 2026: Deepfake Vishing and AI-Generated Phishing
Threat actors deploy generative AI models to synthesize highly convincing voice clones (vishing) and dynamically personalize phishing payloads, bypassing traditional heuristic security controls. This evolution shifts social engineering from static credential harvesting campaigns to dynamic, real-time identity spoofing architectures requiring advanced zero-trust validation. Mechanics of AI-Augmented Social Engineering The integration of Large Language Models (LLMs)…
-
🛡️ The Ultimate Guide to CompTIA Security+ (SY0-701) in 2026
The CompTIA Security+ (SY0-701) certification establishes the definitive global baseline for cybersecurity readiness. It validates the technical proficiency required to design, deploy, and maintain secure enterprise architectures within complex, hybrid environments. As the adversarial landscape accelerates, the SY0-701 exam mandates a structural shift away from implicit-trust, perimeter-based defenses toward data-centric Zero Trust Architectures (ZTA). This…